ISNP
IRDAI audit & compliance for insurance brokers
ISNP Audit for Insurance Brokers. Pass it. Stay compliant all year.
One accountable partner for readiness, the annual IS audit and ongoing compliance. Trusted by 50+ insurance brokers to protect their licence, their data and their growth plans.
Sample readiness snapshot
ISNP audit readiness
82%
Controls audit-ready · 4 open actions
Access control & identity
Ready
Policyholder data protection
In remediation
Hosting & vendor risk
Ready
Logging & incident response
Under review
Every engagement starts with a snapshot like this, so you know exactly where you stand.
Clear scope
Platform, systems, vendors, and evidence
Risk-led review
Priorities based on control gaps and exposure
Defined deliverables
Findings, action plans, and management reporting
Ongoing support
Follow-up reviews and observation tracking
Trusted by leadership at
+47 more
What is ISNP
What is an ISNP audit?
An ISNP audit is an independent review of an insurance intermediary's Insurance Self-Network Platform (ISNP), the website or app used to sell and service policies online. It checks that the platform's security, data protection and operational controls meet IRDAI's requirements, and records the findings in a formal audit report.
IRDAI - Guidelines on Insurance e-commerce irdai.gov.in
The business case
Why the ISNP audit matters: licence, data and growth risk..

Regulatory exposure
Audit observations can lead to regulatory action and slow down approvals. Your Principal Officer is accountable.

Data liability
Your ISNP holds sensitive policyholder data. The DPDP Act raises the cost of getting protection wrong.
Operational drag
Unplanned evidence gathering pulls tech, ops and sales teams away from revenue for weeks.
“Audit readiness starts with knowing your controls, identifying who owns them, and keeping evidence of how they work.”
Services
ISNP audit services: readiness, annual IS audit and ongoing compliance.
Before
4-6 weeks
Audit Readiness
Prepare your ISNP environment, policies, evidence and control framework before the formal audit begins.
Deliverables
Gap assessment against IRDAI Information & Cyber Security Guidelines
Review of policies, procedures and governance structure
Prior-year observation closure validation
Evidence collection support and audit preparation workshops
Risk and control mapping across applicable IRDAI domains
First-Time ISNP Audits, New IRDAI Requirements, Or Major Platform Changes
Best For
During
Annual
Annual IRDAI Cyber Security Audit & VAPT
Independent assessment of your cyber security controls and technical security posture, delivered by qualified auditors and security testers.
Deliverables
Grey-box VAPT of ISNP Web Application
Android Application Security Testing aligned to OWASP MASVS
Infrastructure Security Assessment (Firewall, Servers & Supporting Systems)
Control Testing Across Applicable IRDAI Security Domains
Verification of Prior-Year Observation Closure
Compliance Audit Report and Management Letter
IRDAI Submission-Ready Compliance Certificate
One Round of Confirmatory Re-Testing
every ISNP-operating broker, every year
Best for
Our Approach
A Clear Process from Kickoff to Clean Report
You always know what's happening, who owns it and what you get at each step.
1
Discover
Scoping call with your Principal Officer and tech lead.
→ Scope & plan
2
Assess
Structured gap review of platform, processes and evidence.
→ Readiness snapshot
3
Remediate
Hands-on support, templates and weekly check-ins with your team.
→ Closed gaps
4
Audit
Independent, evidence-based IS audit by qualified auditors.
→ Audit report
5
Sustain
Ongoing monitoring so compliance becomes business as usual.
→ Year-round readiness
Why Rex
Why insurance brokers choose Rex over generalist auditors.
We focus on the insurance broking ecosystem. That means fewer explanations from your side, sharper findings from ours.
CISA
IS audit and controls assurance
ISO 27001
Information security management
CDPO
Data protection and privacy
How we compare
Generalist auditor
Rex Cyber Solutions
ISNP and broker focus
One of many sectors
✓ Core focus
Readiness before the audit
Audit only
✓ Included path
Hands-on remediation help
Findings list
✓ Templates & check-ins
Data protection (DPDP) expertise
Varies
✓ DCDPO on team
Year-round support
Once a year
✓ Named advisor
Your audit team
Meet the ISNP auditors behind your report.
Real people with real credentials. You'll know exactly who is reviewing your platform.
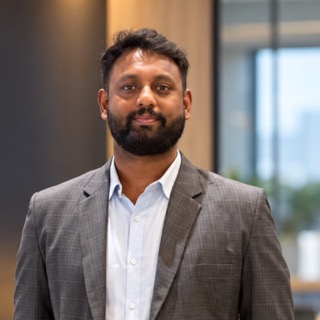
Rex Pushparaj
Lead IS Auditor
Fractional CISO
DPO
Forensic Investigator Turned Compliance Advisor | Leading Cyber Forensics, Risk Mitigation, and Regulatory Compliance Engagements
10+ years · Bengaluru
LinkedIn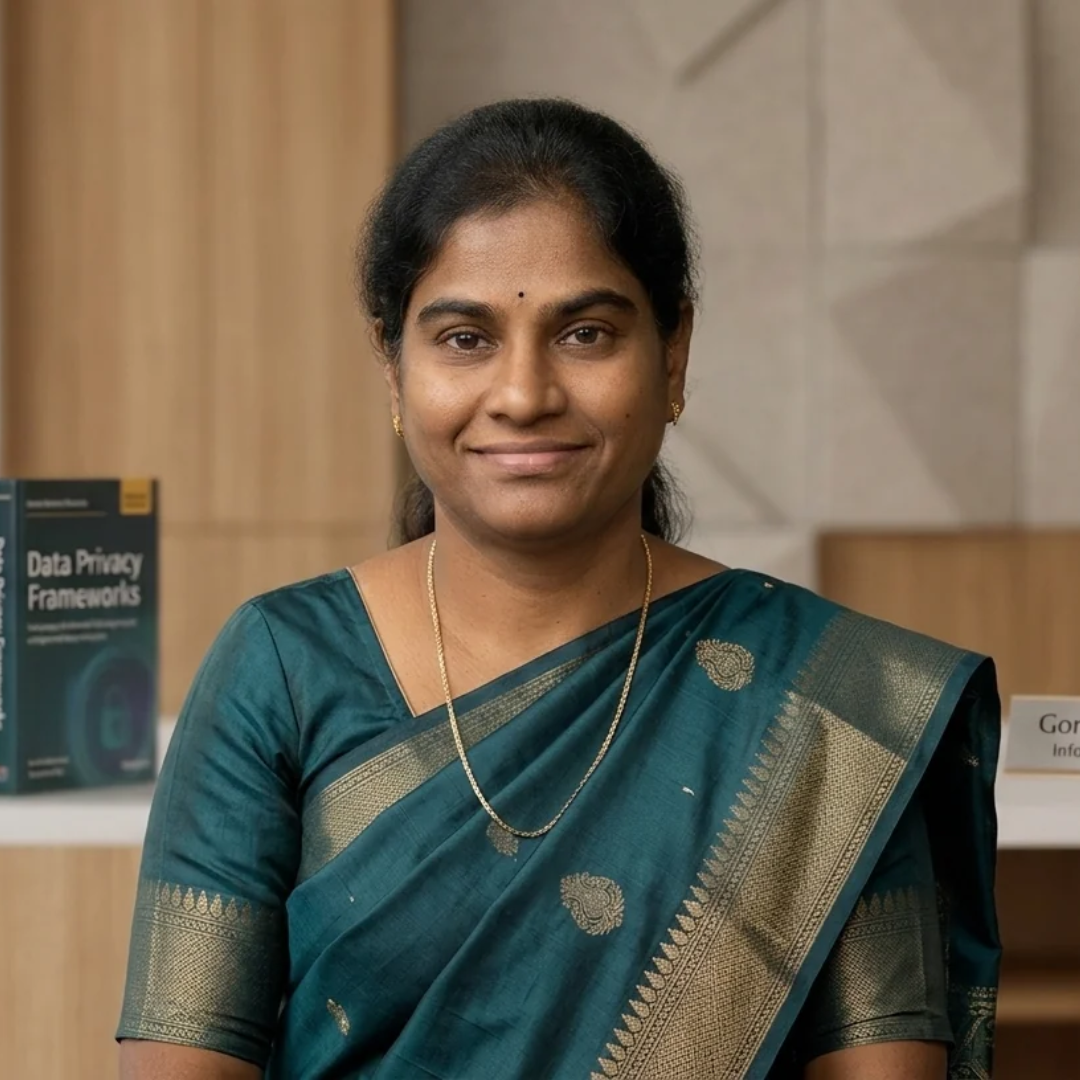
Gomathi Shanmugam
Lead Auditor
CISA
iso 27001
Information Security Advisor | Leading Enterprise IS Audits, Risk Assessments, and Stakeholder Security Engagements
15+ years · Ontario
LinkedInClient voices
What insurance broker leaders say about Rex.

"Rex Cybersecurity simplified our ISNP audit process completely. Their team demonstrated a thorough understanding of IRDAI compliance guidelines, delivering an efficient audit that strengthened our digital security posture without interrupting our daily brokerage operations."
RC
Ravichandran.P
Principal Officer, Moneys Spidery
"Partnering with Rex Cyber Solutions gave us complete clarity on our cybersecurity and regulatory readiness. Their ISNP audit insights were practical, precise, and executed with high professionalism from scope definition to final certification."
SR
Sanjay Revalkar
CEO, Godspeed Insurance
"Rex Cyber Solutions proved to be an invaluable security partner. They handled our ISNP audit seamlessly, identifying vulnerabilities, ensuring full IRDAI compliance, and giving our clients absolute confidence in our digital infrastructure."
SH
Shriram
CEO, Arka Insurance Brokers
FAQ
ISNP Audit Questions, answered
Practical answers about audit scope, preparation, technology partners, and next steps.
Discuss Your Audit
01
What does an ISNP audit cover?
02
Is an ISNP audit required, and how often?
03
Who can conduct the review?
04
Which documents should we prepare?
05
Our platform is built and hosted by a vendor. Can you help?
06
How long does the engagement take, and what does it cost?
07
Can we choose only readiness or ongoing support?
Get Started
Know What Your ISNP Needs Before the Audit Begins
Tell us about your platform, technology partners, and upcoming audit. We’ll help you define the scope, identify the evidence to prepare, and agree the next steps.

For insurance brokers preparing for an audit or strengthening ongoing compliance.

Sign up to receive the latest security news and trends straight to your inbox from Rex Cybersolutions.



D‑U‑N‑S® NUMBER:
876730103
